Sales: +91 9600 70 3224
- Support


SSH, RDP, MySQL, PostgreSQL, MongoDB, Kubernetes and web targets, recorded end to end.
No session runs directly between a user and a target. AkkuReka sits in the path, and because it sits in the path it can record what happened, log every command, and cut the connection while it is still open. The target sees the proxy, not the person, and never knows the real user's identity.
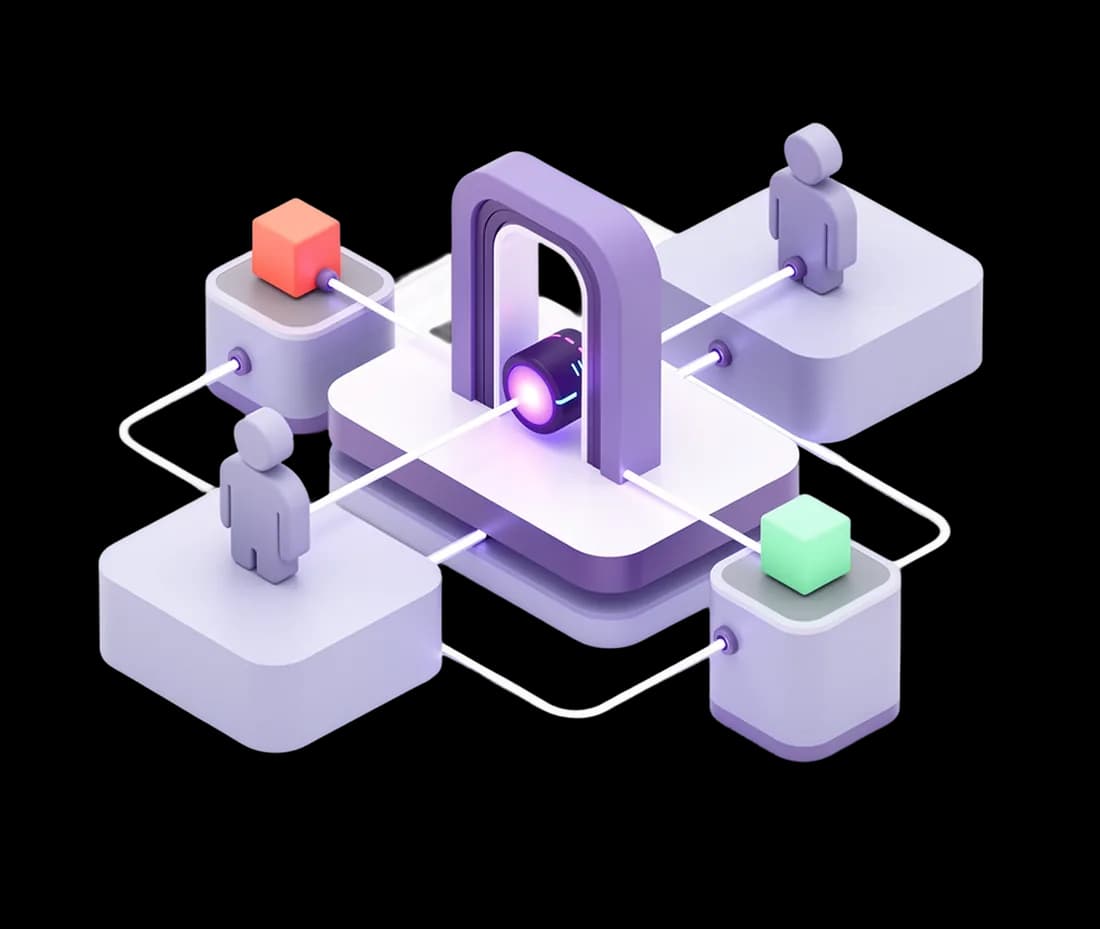
SSH to Linux, Unix and network devices, with full screen capture and a complete keystroke log per command. RDP to Windows servers and desktops, with screen video at a frame rate you set. MySQL, PostgreSQL and MongoDB, with screen capture plus every query stored as structured data rather than as pixels. Kubernetes, natively, with the command log. And HTTP and HTTPS for web applications. Coverage expands, so confirm the current list for a specific environment.
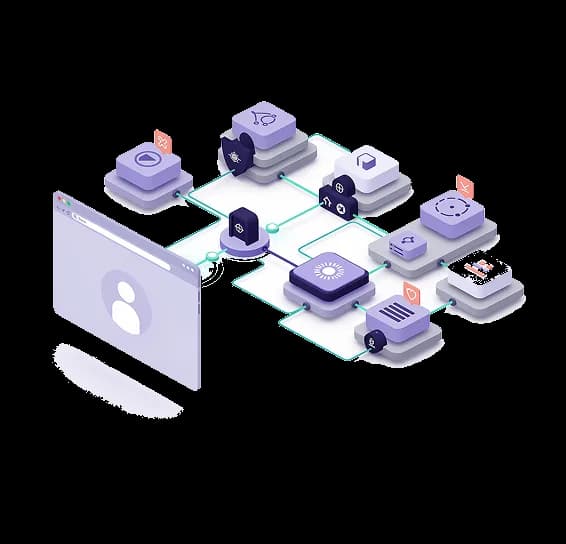
Recordings stream to encrypted storage as the session runs, indexed for playback in the console with no media player and no download. Each carries the session ID, the actor, the target, start and end timestamps, duration and the reason it ended. Forensic search runs inside recordings by timestamp, by command string or by SQL query, so finding the moment someone dropped a table is a search rather than a viewing.
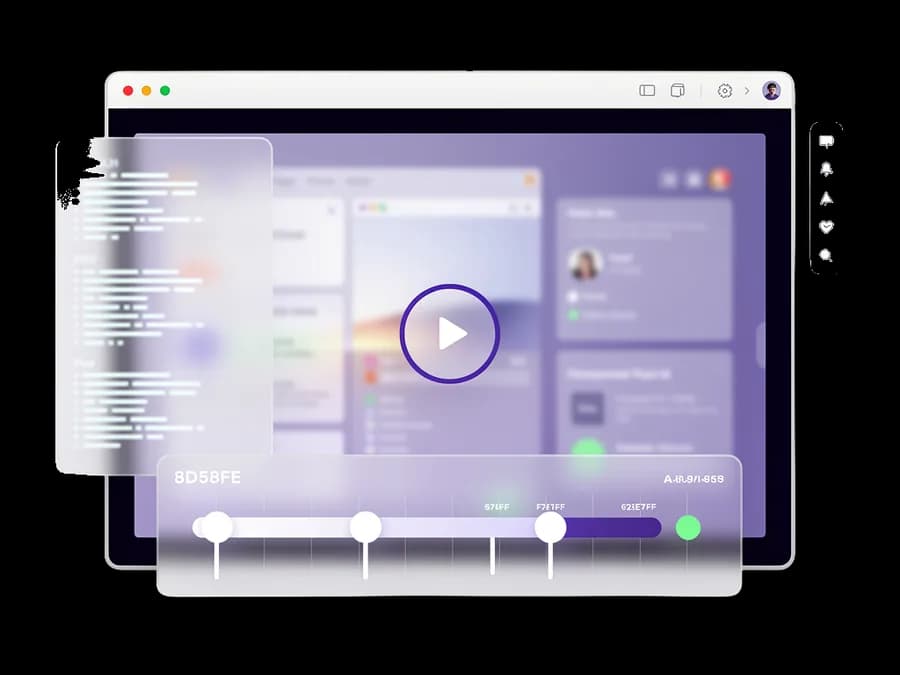
Every active session is visible in the console as it happens. Any of them can be terminated instantly, severed at the proxy rather than requested politely of the target. The termination is written to the audit log with the actor, the timestamp and the reason, the session is flagged in history, and the recording remains available in full.
Targets need no agent. The worker reaches them over their existing ports, and they are never directly reachable from the internet.