Sales: +91 9600 70 3224
- Support


Seven policy signals evaluated before a session opens, an approver in the path when you want one, and access that expires on its own.
Access is granted for the duration of one approved session and then it is gone. There is no persistent privilege on a target to inherit, to forget about, or to find in a leaver's account six months later. What decides whether a session opens is a policy evaluated at the moment it is requested.
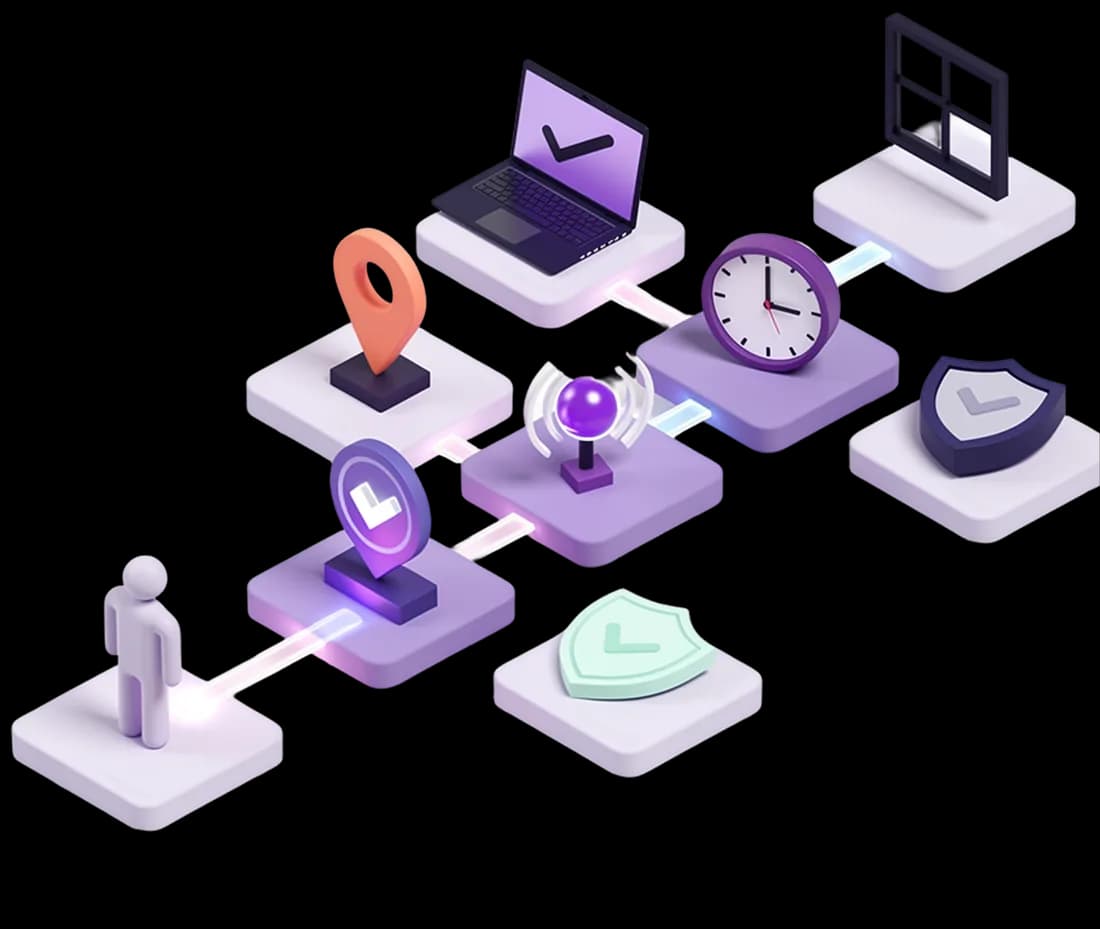
Seven signals, in combination. Whether the device is registered and compliant with your MDM policy. Whether the user's location is inside permitted boundaries. Whether the source IP is on a blocked list. Whether the request falls inside the permitted hours for that role. Whether the access pattern matches the user's own history. Whether their role permits that target at all. And whether an approved JIT window is currently open. Failing one signal denies the request, or steps up to MFA, depending on the signal and what you set.
TOTP through any authenticator app, push through the Akku mobile app, Cisco Duo, hardware tokens on OATH, and YubiKey over FIDO2 and WebAuthn. MFA sits at the identity layer, which is why it applies to a privileged session the same way it applies to any application behind sign-in.
Where approval is enabled, a request carries the target, the access level, the duration and the user's justification, and the session stays pending until someone acts. Approvers are notified by email or in the platform. Approvals and denials are logged with the approver's identity and the timestamp. On approval the session opens and the credential is generated at that point, not before.
A role specifies the targets it permits, the protocols, the permitted hours, and the maximum JIT duration. The credential AkkuArka generates is scoped to the minimum permission the session role requires. And a permitted-command list limits what can be run inside the session, with blocked attempts logged as failed rather than silently dropped.
A JIT session is time-bound from the moment of approval. On expiry the session terminates, the credential is revoked, and access is removed without anyone remembering to remove it. Request time, approval time, session start, session end and credential revocation are each timestamped.