Sales: +91 9600 70 3224
- Support


Self-registration with social sign-in, consent recorded per purpose, and integration through APIs and SDKs.
Akku CIAM handles the identity of the people outside your business: customers registering, signing in, and deciding what you may do with their data. Registration is self-service with social sign-in, reinforced by adaptive MFA where the risk warrants it. Consent is captured against a register of what you collect and why, withdrawal takes one action, and every change leaves a record. It embeds into your customer-facing applications through REST APIs, SDKs and pre-built connectors rather than sitting beside them.
Customer identity and access management is the identity layer for the people who use your public-facing applications rather than the people who work for you. It covers how someone creates an account, how they prove who they are on return, what they have agreed to, and how they exercise the rights they hold over their own data. The reason it is separate from workforce identity is that the population is different in kind. Customers are not onboarded, the numbers are far larger, and what you may do with their data rests on consent they gave and can withdraw. That last point is why CIAM carries most of what the DPDP Act asks of a data fiduciary.
Accounts customers create themselves, verified as they do.
Guided self-service registration with social sign-in from the major providers, so an account gets created without anyone in your business provisioning it. MFA is available on customer accounts, and adaptive MFA applies it selectively, so a routine sign-in stays routine and an unusual one meets a second factor. Identity creation is consistent across every channel a customer arrives through.
Learn more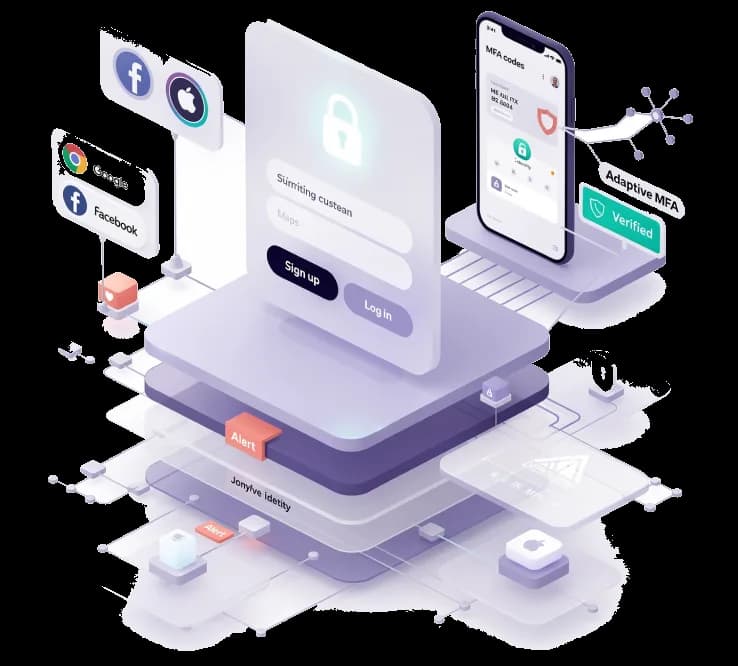
Consent per purpose, withdrawal in one action, and a record of both.
Consent is captured against a versioned register of what you collect and why, recorded per data item against a lawful basis. Withdrawal is a single control in the self-service portal, and the signal propagates to your downstream systems and processors. Data principal rights, verifiable parental consent and grievance handling are covered, and every consent event is held as a tamper-evident record.
Learn more
Embedded in your applications, not sitting beside them.
Documented REST APIs cover the full identity lifecycle for anything you are building yourself, developer SDKs shorten the work where a supported language fits, and pre-built connectors onboard common applications without custom integration. The same authentication and the same consent state apply across every integrated channel.
Learn more
Customer identity gets traffic patterns workforce identity never sees: a campaign, a product launch, a renewal deadline. The platform is built for large customer bases and holds a consistent authentication experience through spikes, with per-client throttling and rate limiting protecting it from both misuse and accidental overload.
Consent Manager carries most of what the DPDP Act asks of a data fiduciary: consent recorded against a lawful basis per data item, withdrawal made as easy as giving it, verifiable parental consent, and erasure that carries through to your processors. It also covers all 18 of SOC 2's Privacy criteria, from notice and consent capture through to disclosure records and breach notification. The clause-level detail for both sits in the compliance section.
Learn more