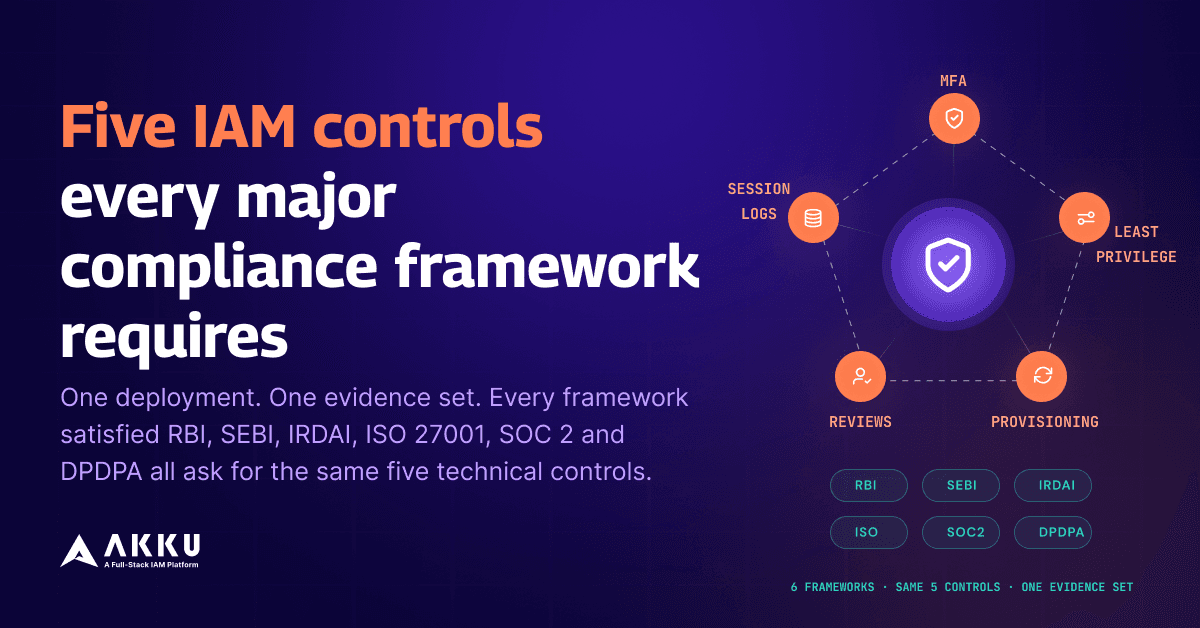
Five IAM Controls Every Major Compliance Framework Requires
Vinayak P

Five IAM Controls Every Major Compliance Framework Requires

Your organisation is likely operating under more than one compliance framework. RBI if you are a bank or NBFC. SEBI CSCRF if you are a capital markets entity. IRDAI ICS if you are an insurer. ISO 27001 if you are pursuing certification. SOC 2 if you serve enterprise clients. DPDPA if you process personal data … Continue reading Five IAM Controls Every Major Compliance Framework Requires
10 July 2026|13 min read
What DPDPA Actually Requires From Your IT Team
Vinayak P

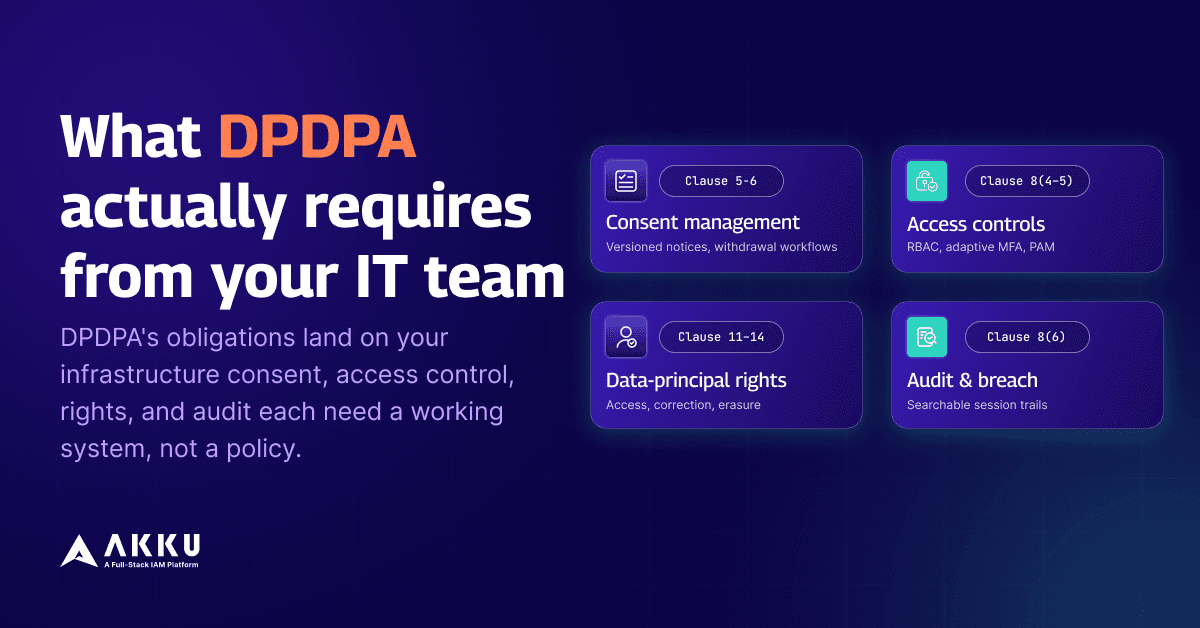
What DPDPA Actually Requires From Your IT Team

The Digital Personal Data Protection Act, 2023 is not a policy compliance exercise. The obligations it creates land directly on your IT infrastructure. Consent must be captured, stored, and made withdrawable through a technical system. Access to personal data must be controlled and auditable. Data Principal rights including access, correction, and erasure require automated workflows … Continue reading What DPDPA Actually Requires From Your IT Team

06 July 2026|12 min read
Identity Fragmentation: The Hidden Cost of Managing IAM Across Multiple Applications
Yeswanth A

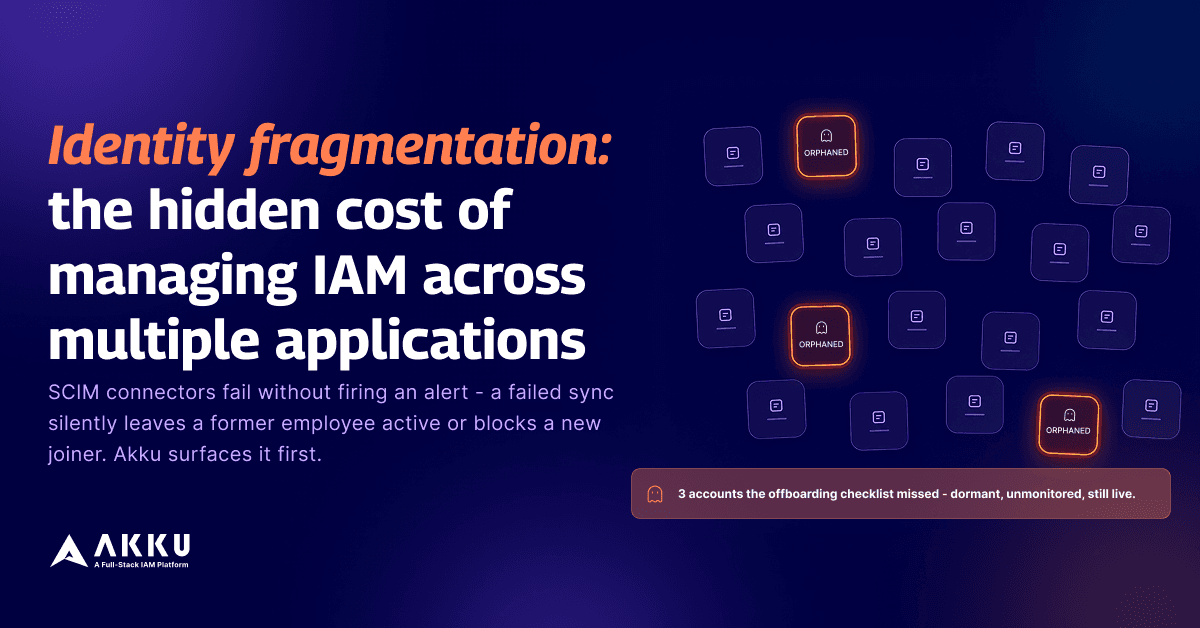
Identity Fragmentation: The Hidden Cost of Managing IAM Across Multiple Applications

Your organisation has forty-three applications. Each one manages its own users. Each one has its own provisioning process, its own access review cycle, its own offboarding checklist item, and its own audit log in its own format. In normal operations, this is manageable. Imperfectly, slowly, with more manual effort than any IT team would choose, … Continue reading Identity Fragmentation: The Hidden Cost of Managing IAM Across Multiple Applications

29 June 2026|12 min read
PAM Coverage Gaps on Linux: Why SSH Sessions Are Your Highest-Risk Ungoverned Access
Vinayak P

PAM Coverage Gaps on Linux: Why SSH Sessions Are Your Highest-Risk Ungoverned Access

Your PAM platform covers privileged access. Ask your infrastructure team how much of it, and the answer will involve a percentage. Ask which systems are excluded, and the answer will almost certainly include Linux servers accessed directly over SSH. PAM coverage metrics count the accounts that are under management on the PAM platform. A Windows … Continue reading PAM Coverage Gaps on Linux: Why SSH Sessions Are Your Highest-Risk Ungoverned Access

29 June 2026|12 min read
SCIM Connector Failures Are Silent. The Access Gaps They Leave Are Not.
Yeswanth A

SCIM Connector Failures Are Silent. The Access Gaps They Leave Are Not.

Your SCIM provisioning connector ran its last sync six hours ago. It failed. Nobody received an alert. Nobody knows. The employee who left the organisation this morning still has active entitlements in the three applications connected through that SCIM integration. The access revocation that should have happened at offboarding ran, the IGA platform recorded the … Continue reading SCIM Connector Failures Are Silent. The Access Gaps They Leave Are Not.

22 June 2026|13 min read
Android MDM Background Location Tracking: Why Foreground-Only APIs Miss Most of the Shift
Vinayak P

Android MDM Background Location Tracking: Why Foreground-Only APIs Miss Most of the Shift

Your MDM platform reports device location. What it does not tell you is how much of the shift that location data actually covers. Android distinguishes between foreground location and background location at the API level. Foreground location APIs deliver updates while the requesting application is the active process on the device screen. The moment the … Continue reading Android MDM Background Location Tracking: Why Foreground-Only APIs Miss Most of the Shift

22 June 2026|12 min read
Your Offboarding Checklist Has a Gap. It’s Called SAP.
Yeswanth A

Your Offboarding Checklist Has a Gap. It’s Called SAP.

What is the most sensitive system in your organisation? Not the most technically complex. The one with the highest concentration of data that would cause the most damage if a former employee retained access to it after leaving. For most manufacturing, financial services, and retail organisations, the answer is SAP. The general ledger. Accounts payable. … Continue reading Your Offboarding Checklist Has a Gap. It’s Called SAP.

15 June 2026|10 min read
Audit-Ready Organisations Don’t Prepare for Audits. They’re Already Ready.
Vinayak P

Audit-Ready Organisations Don’t Prepare for Audits. They’re Already Ready.

Here is a question worth asking your compliance team: how long would it take to produce the evidence package for your next ISO 27001 or SOC 2 audit if the auditor announced it today? If the answer is measured in weeks, your organisation is not compliant. It is compliant-looking, periodically, when someone assembles the evidence. … Continue reading Audit-Ready Organisations Don’t Prepare for Audits. They’re Already Ready.

15 June 2026|11 min read
Access Layer Authentication Does Not Extend to Data Exfiltration Controls.
Yeswanth A

Access Layer Authentication Does Not Extend to Data Exfiltration Controls.

Your BYOD policy permits employees to access corporate applications from personal devices. The security team agreed to this because blocking personal device access was creating friction that hurt productivity. The IT team agreed because enforcing full MDM enrollment on personal devices was operationally impractical and legally contested in some jurisdictions. What neither team thought through … Continue reading Access Layer Authentication Does Not Extend to Data Exfiltration Controls.

08 June 2026|8 min read

Keep in Touch

Sign up for our blogs