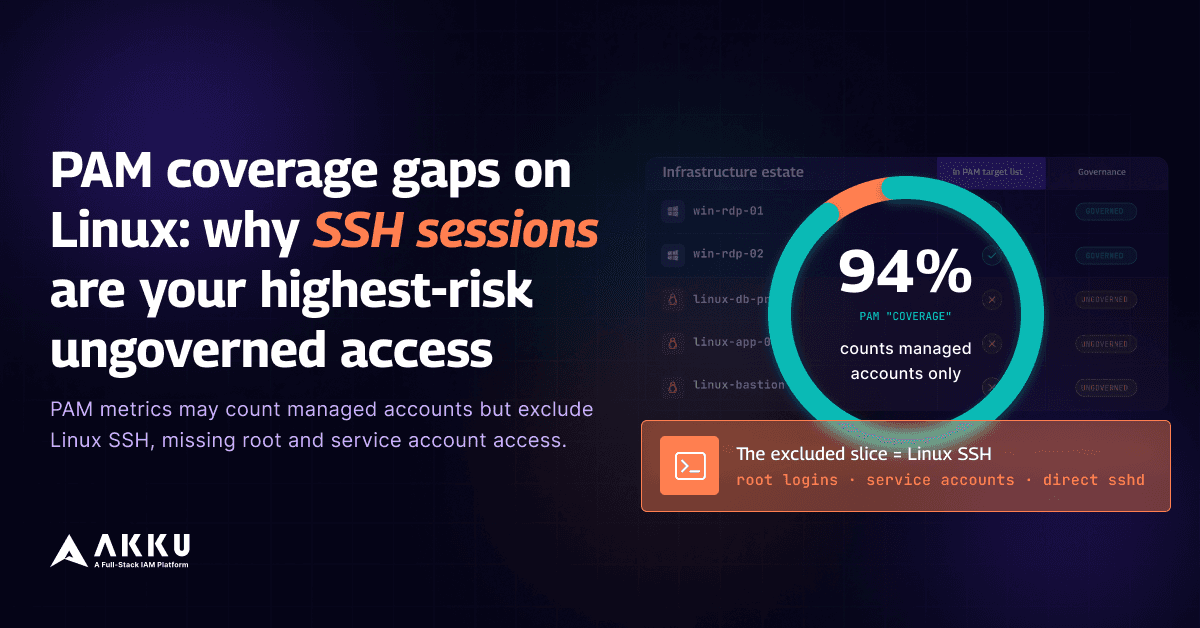
PAM Coverage Gaps on Linux: Why SSH Sessions Are Your Highest-Risk Ungoverned Access
Vinayak P

PAM Coverage Gaps on Linux: Why SSH Sessions Are Your Highest-Risk Ungoverned Access

Your PAM platform covers privileged access. Ask your infrastructure team how much of it, and the answer will involve a percentage. Ask which systems are excluded, and the answer will almost certainly include Linux servers accessed directly over SSH. PAM coverage metrics count the accounts that are under management on the PAM platform. A Windows … Continue reading PAM Coverage Gaps on Linux: Why SSH Sessions Are Your Highest-Risk Ungoverned Access
29 June 2026|12 min read
SSH Session Logging and Authentication Logging Are Not the Same Control.
Yeswanth A

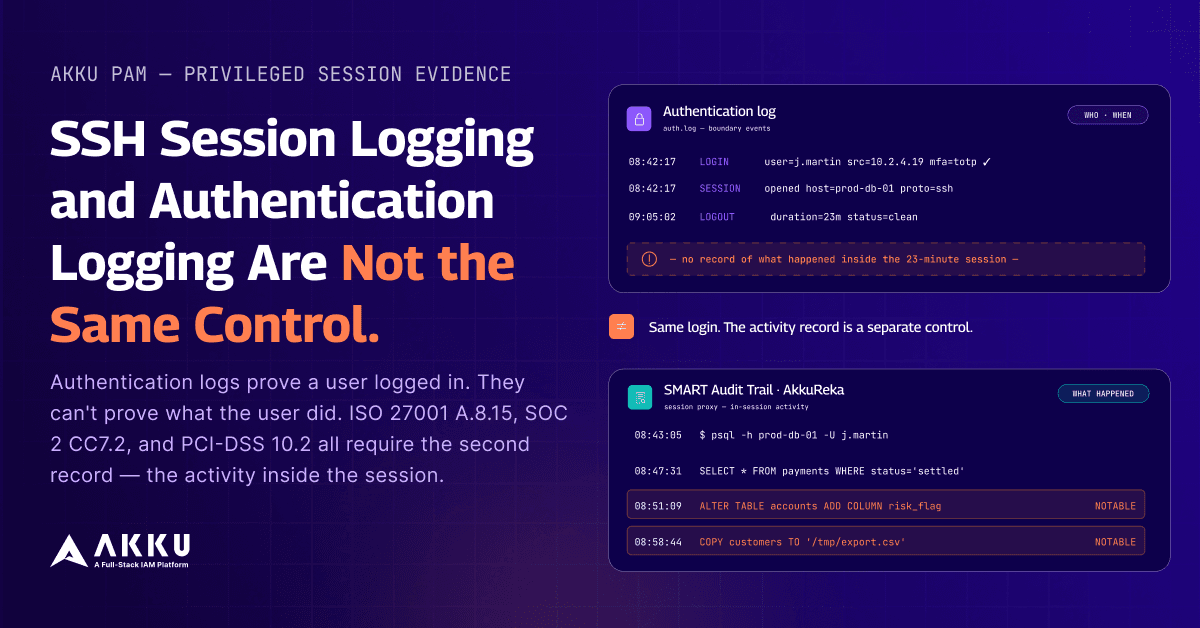
SSH Session Logging and Authentication Logging Are Not the Same Control.

A security incident investigation is three days in. A privileged user accessed a production database server on a Tuesday afternoon. Something changed on that server that caused a downstream service failure two days later. The authentication log shows the login event. Username, timestamp, source IP, session duration. 23 minutes. The session ended cleanly. Nothing else … Continue reading SSH Session Logging and Authentication Logging Are Not the Same Control.

08 June 2026|9 min read
MFA Verified the User. Nobody Verified the Device.
Vinayak P

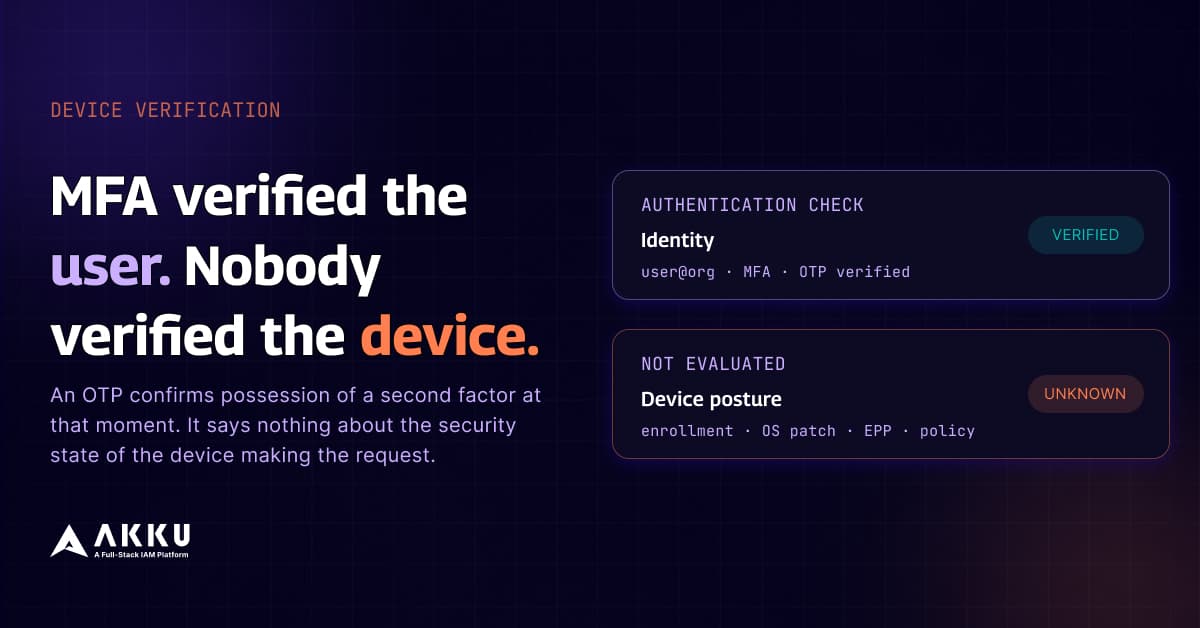
MFA Verified the User. Nobody Verified the Device.

Your user authenticated this morning. They presented the right credentials. They completed the MFA challenge. Your access control system granted the session. Here is what your authentication stack evaluated during that process: the identity of the person requesting access. Here is what it did not evaluate: the security posture of the device they used to … Continue reading MFA Verified the User. Nobody Verified the Device.

13 May 2026|10 min read
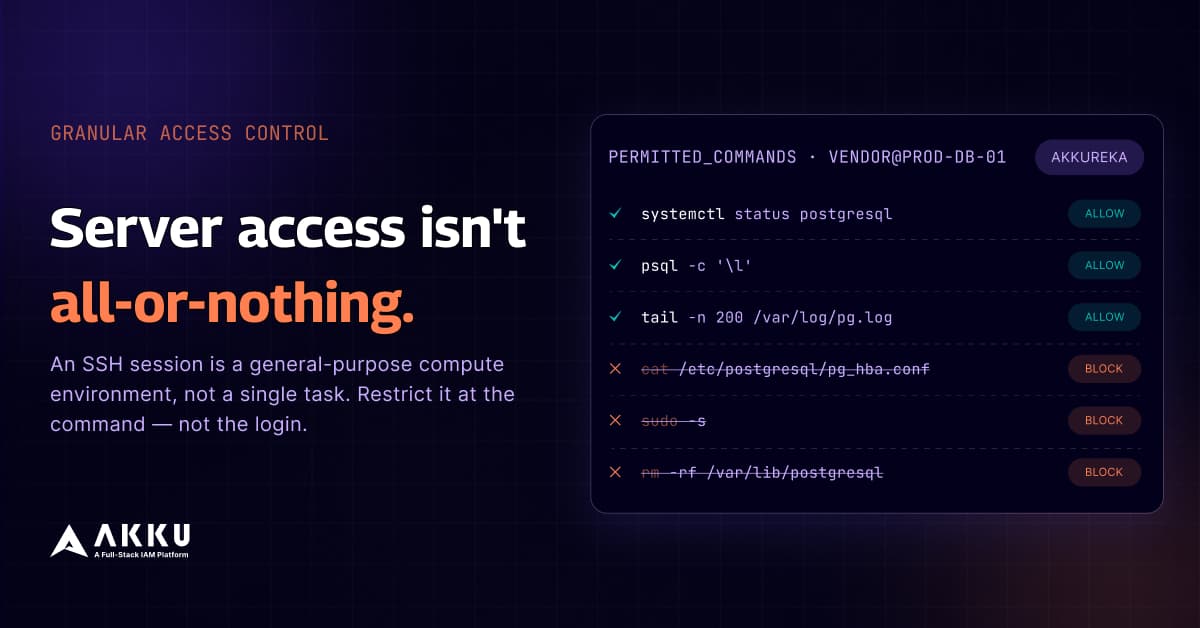
Server Access Isn’t All-or-Nothing. The Organisations Treating It That Way Have a Problem.
Yeswanth A

Server Access Isn’t All-or-Nothing. The Organisations Treating It That Way Have a Problem.

When you give someone SSH access to a Linux server, what exactly have you given them? Think about that carefully before answering. Because the instinct is to say “access to do the thing they were brought in to do.” But what the SSH session actually provides, absent any command-level restrictions, is an interactive shell with … Continue reading Server Access Isn’t All-or-Nothing. The Organisations Treating It That Way Have a Problem.

13 May 2026|11 min read
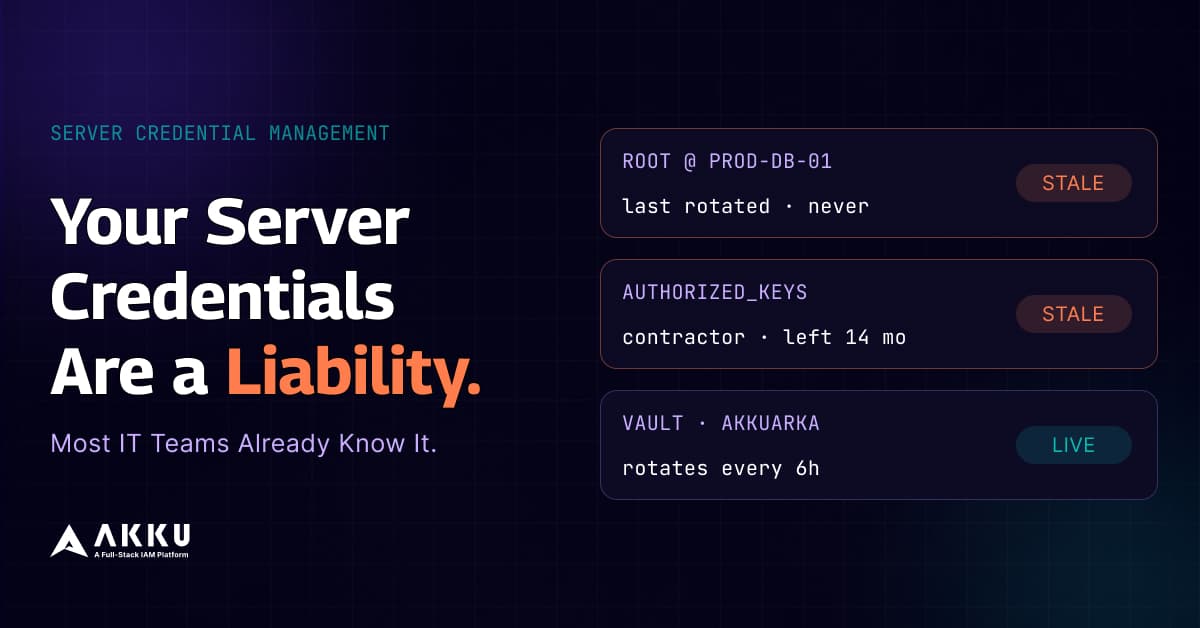
Your Server Credentials Are a Liability. Most IT Teams Already Know It.
Dinesh Harikrishnan

Your Server Credentials Are a Liability. Most IT Teams Already Know It.

When did you last rotate the root password on your most critical production server? Not when it was scheduled. Not when the policy says it should have been. When it actually happened, with a documented record, and with every system that depended on that credential updated at the same time. If that question made you … Continue reading Your Server Credentials Are a Liability. Most IT Teams Already Know It.

13 May 2026|11 min read
Is Your PAM Solution Built on a Remote Desktop Gateway?
SatyaDev Addeppally

Is Your PAM Solution Built on a Remote Desktop Gateway?

If you are currently evaluating Privileged Access Management solutions, there is a question worth asking the vendors in your shortlist: what is this product actually built on? Not every PAM solution on the market was built from the ground up as a PAM platform. Some are remote desktop gateways with PAM features bolted on. Some … Continue reading Is Your PAM Solution Built on a Remote Desktop Gateway?

06 May 2026|7 min read
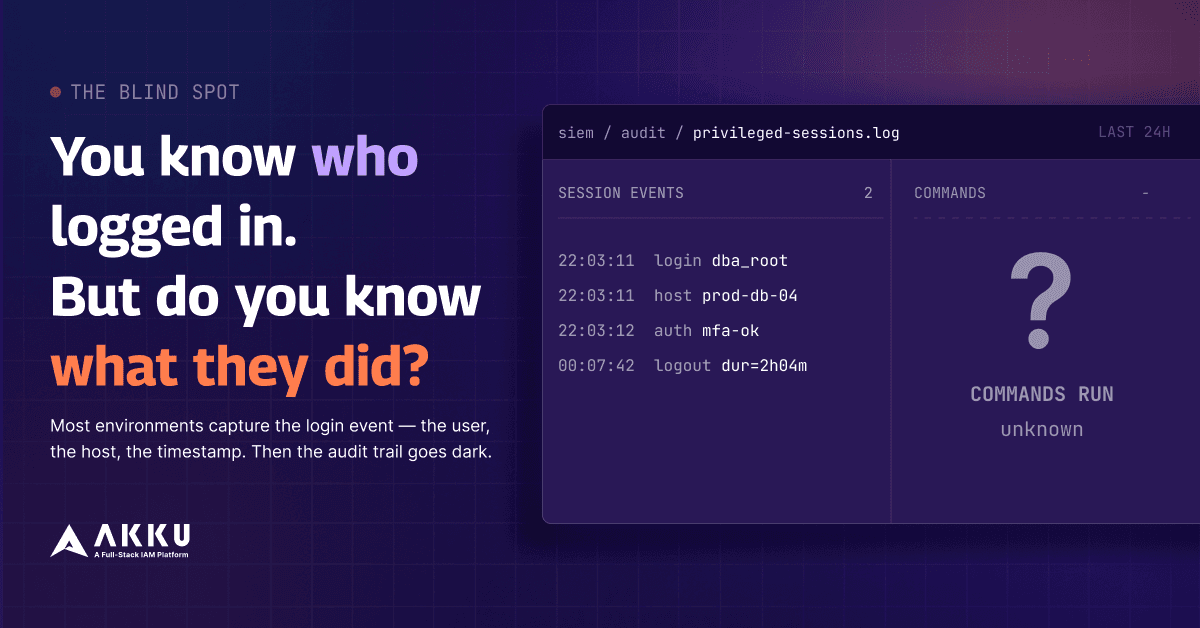
You Know Who Logged In. But Do You Know What They Did?
Dinesh Harikrishnan

You Know Who Logged In. But Do You Know What They Did?

You probably think you know what your admins are doing on your servers. Here is what your logs are actually showing you. A name. A timestamp. A session duration. That’s it. Forty-one minutes on a production server, and your audit trail tells you someone was there. It doesn’t tell you what they typed. What they … Continue reading You Know Who Logged In. But Do You Know What They Did?

05 May 2026|6 min read
Still don’t have PAM in 2026? Here are 10 reasons you need it today!
Yeswanth A

Still don’t have PAM in 2026? Here are 10 reasons you need it today!

In today’s high-stakes cybersecurity environment, privileged accounts control access to your most critical systems and sensitive data. Poor management or insufficient oversight of these accounts creates easy targets for cyberattackers, leading to costly breaches and compliance failures.  According to the 2025 Verizon Data Breach Investigations Report (DBIR), 22% of data breaches in 2025 involved stolen/compromised … Continue reading Still don’t have PAM in 2026? Here are 10 reasons you need it today!

05 February 2026|4 min read
How to Implement Privileged Access Management (PAM) in Cloud and Hybrid Environments
Yeswanth A

How to Implement Privileged Access Management (PAM) in Cloud and Hybrid Environments

Privileged accounts are an under-recognized center of risk in modern IT. The move to cloud and hybrid environments multiplies the number of privileged accounts, and an overlooked admin credential on a single system can become a path to the entire estate. In this article, we examine privileged access management (PAM) and how to approach privileged … Continue reading How to Implement Privileged Access Management (PAM) in Cloud and Hybrid Environments

07 October 2025|7 min read

Keep in Touch

Sign up for our blogs