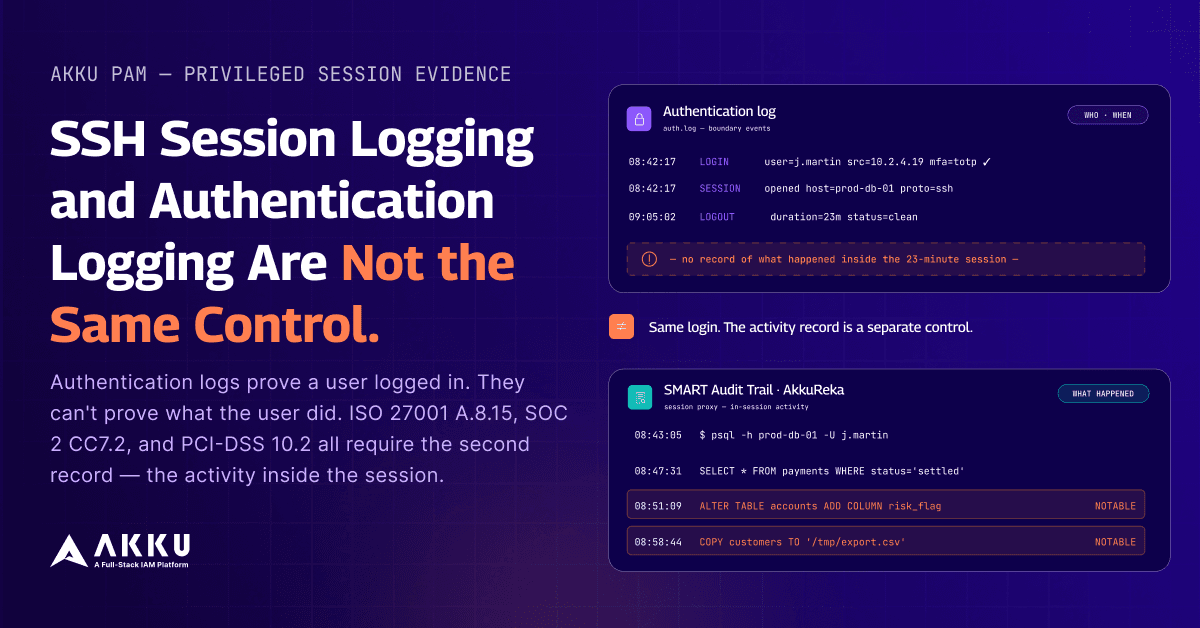
SSH Session Logging and Authentication Logging Are Not the Same Control.
Yeswanth A

SSH Session Logging and Authentication Logging Are Not the Same Control.

A security incident investigation is three days in. A privileged user accessed a production database server on a Tuesday afternoon. Something changed on that server that caused a downstream service failure two days later. The authentication log shows the login event. Username, timestamp, source IP, session duration. 23 minutes. The session ended cleanly. Nothing else … Continue reading SSH Session Logging and Authentication Logging Are Not the Same Control.
08 June 2026|9 min read
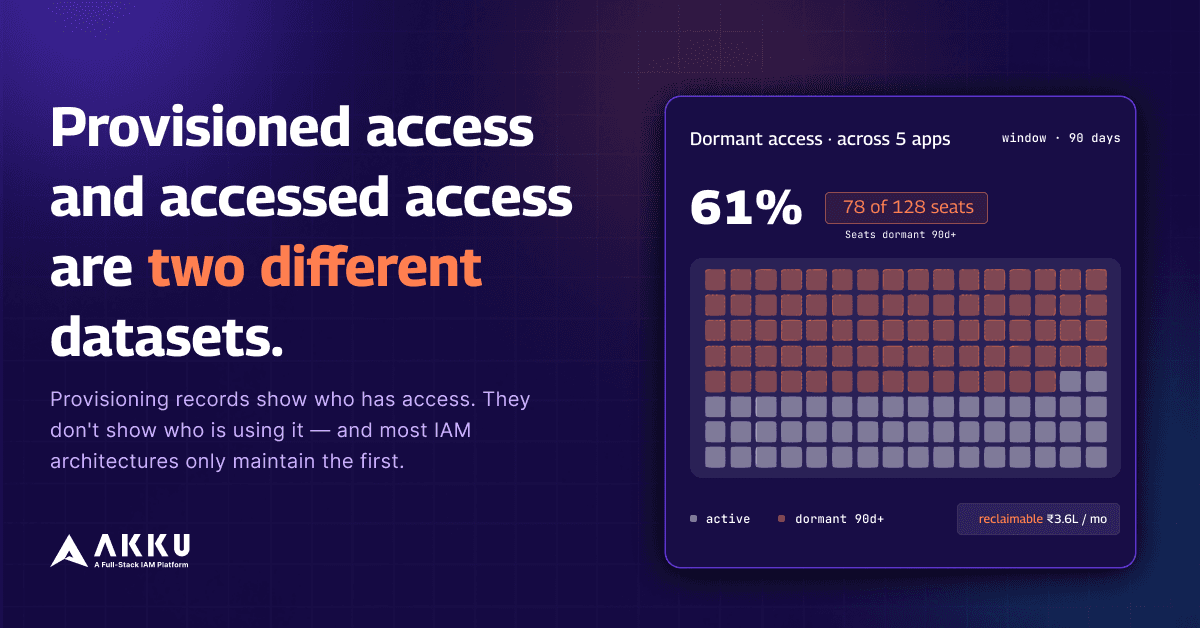
Provisioned Access and Accessed Access Are Two Different Datasets.
SatyaDev Addeppally

Provisioned Access and Accessed Access Are Two Different Datasets.

A provisioning record captures a point-in-time entitlement decision: this user was granted access to this application on this date. It records that the door was opened. It contains no information about whether anyone has walked through it since. An access usage record captures an event: this user authenticated and launched this application at this timestamp … Continue reading Provisioned Access and Accessed Access Are Two Different Datasets.

29 May 2026|11 min read
Authentication Visibility Stops Where Your Monitoring Stack Ends.
SatyaDev Addeppally

Authentication Visibility Stops Where Your Monitoring Stack Ends.

If your SSO platform had a service disruption at 2am tonight, how would your team find out about it? For most IT operations and security teams, the honest answer is: when the support tickets start arriving in the morning. Someone arrives at work, tries to log in, fails, and raises a ticket. By the time … Continue reading Authentication Visibility Stops Where Your Monitoring Stack Ends.

29 May 2026|10 min read
IAM Authentication Events Are Absent From Most SIEM Detection Pipelines.
Yeswanth A

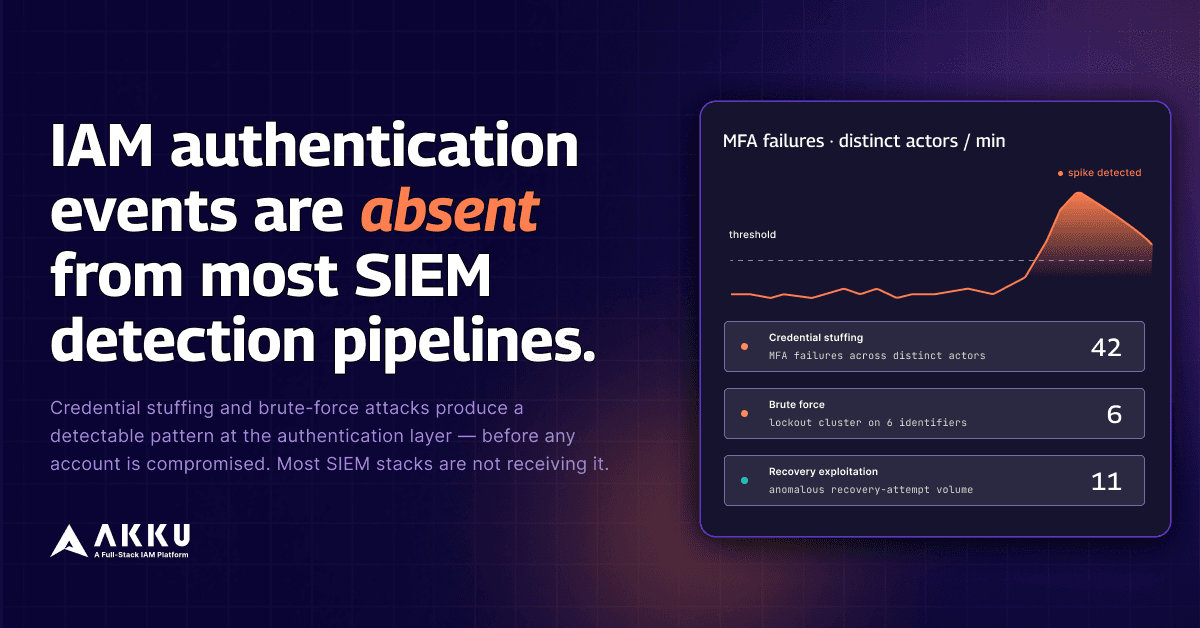
IAM Authentication Events Are Absent From Most SIEM Detection Pipelines.

The IAM layer generates the earliest detectable signal of a credential attack. Before any account is compromised, before any privileged session is opened, before any data is accessed, the attack produces a pattern in the authentication event stream: MFA failure spikes across multiple distinct account identifiers, account lockout clusters on targeted identifiers, or anomalous recovery … Continue reading IAM Authentication Events Are Absent From Most SIEM Detection Pipelines.

29 May 2026|10 min read
Informal Access Provisioning Produces No Defensible Audit Evidence.
SatyaDev Addeppally

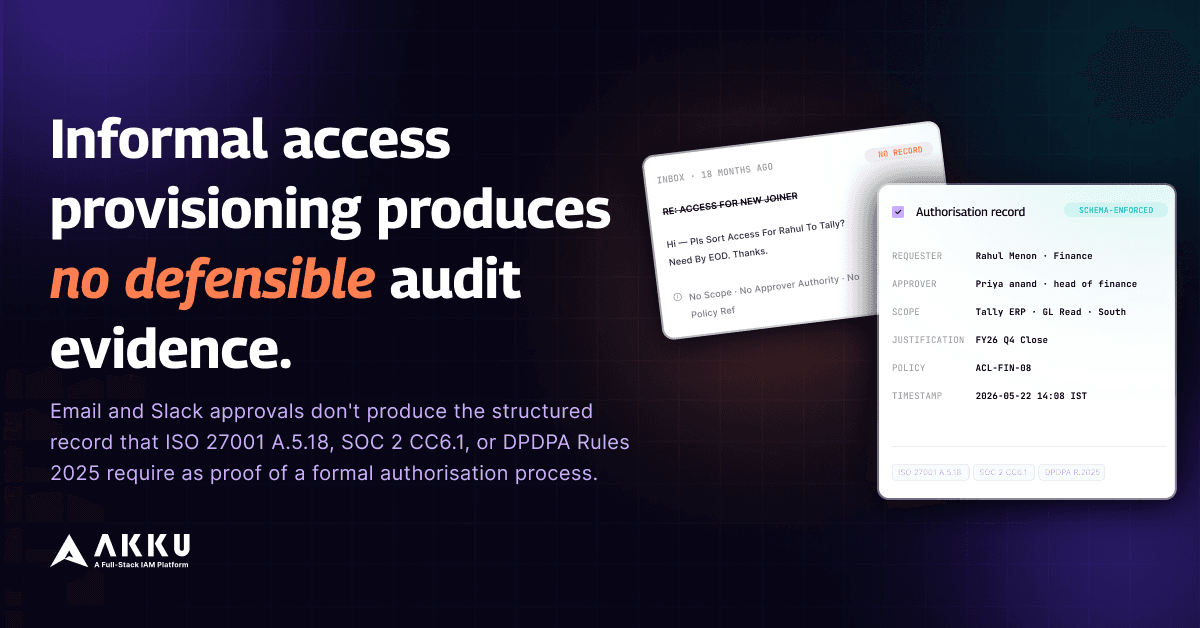
Informal Access Provisioning Produces No Defensible Audit Evidence.

Defensible audit evidence for an access grant has a specific technical definition. It is not a confirmation that the access exists. It is not a record that the access was provisioned. It is a structured record of a formal authorization decision: the identity of the person who approved the access, their authority to approve it, … Continue reading Informal Access Provisioning Produces No Defensible Audit Evidence.

29 May 2026|11 min read
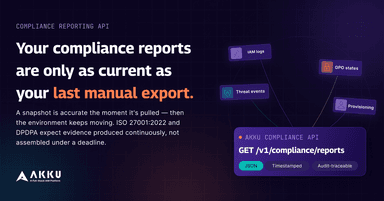
Your Compliance Reports Are Only as Current as Your Last Manual Export
Vinayak P

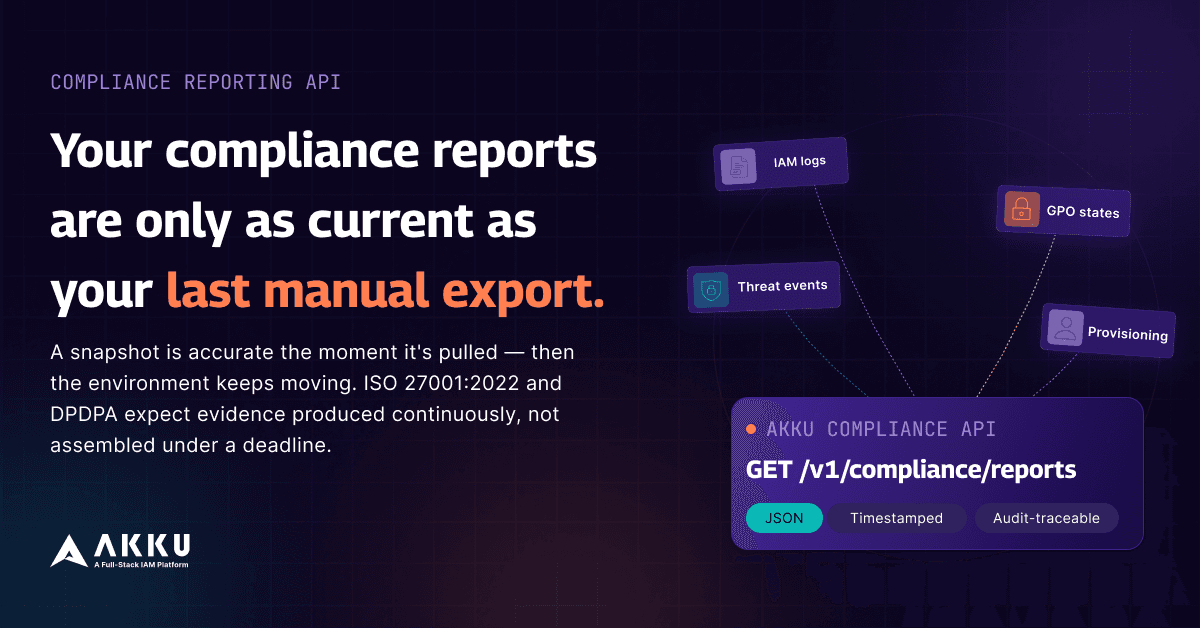
Your Compliance Reports Are Only as Current as Your Last Manual Export

When did you last run a compliance evidence collection that did not surface something unexpected? Not a gap in your controls. Something more mundane than that. A SCIM connector that failed three weeks ago that nobody noticed because there was no monitoring on it. A provisioning record that shows an offboarded user as deprovisioned, but … Continue reading Your Compliance Reports Are Only as Current as Your Last Manual Export

22 May 2026|14 min read
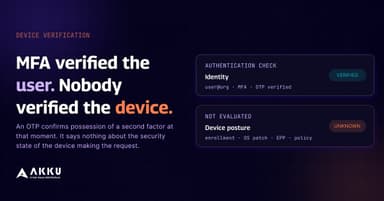
MFA Verified the User. Nobody Verified the Device.
Vinayak P

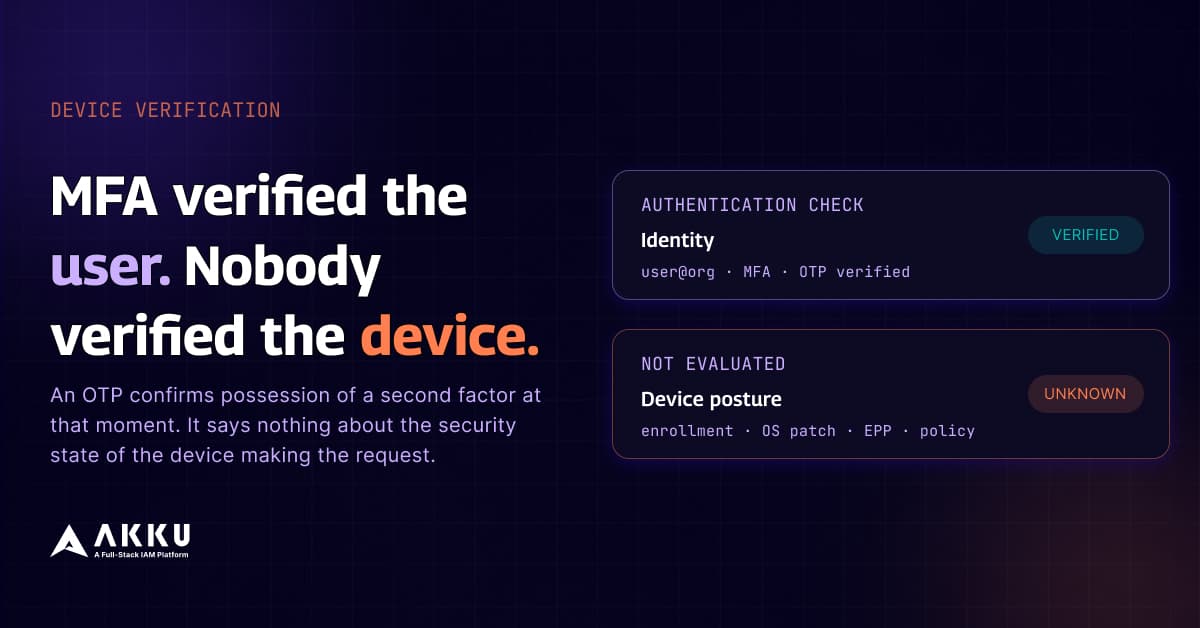
MFA Verified the User. Nobody Verified the Device.

Your user authenticated this morning. They presented the right credentials. They completed the MFA challenge. Your access control system granted the session. Here is what your authentication stack evaluated during that process: the identity of the person requesting access. Here is what it did not evaluate: the security posture of the device they used to … Continue reading MFA Verified the User. Nobody Verified the Device.

13 May 2026|10 min read
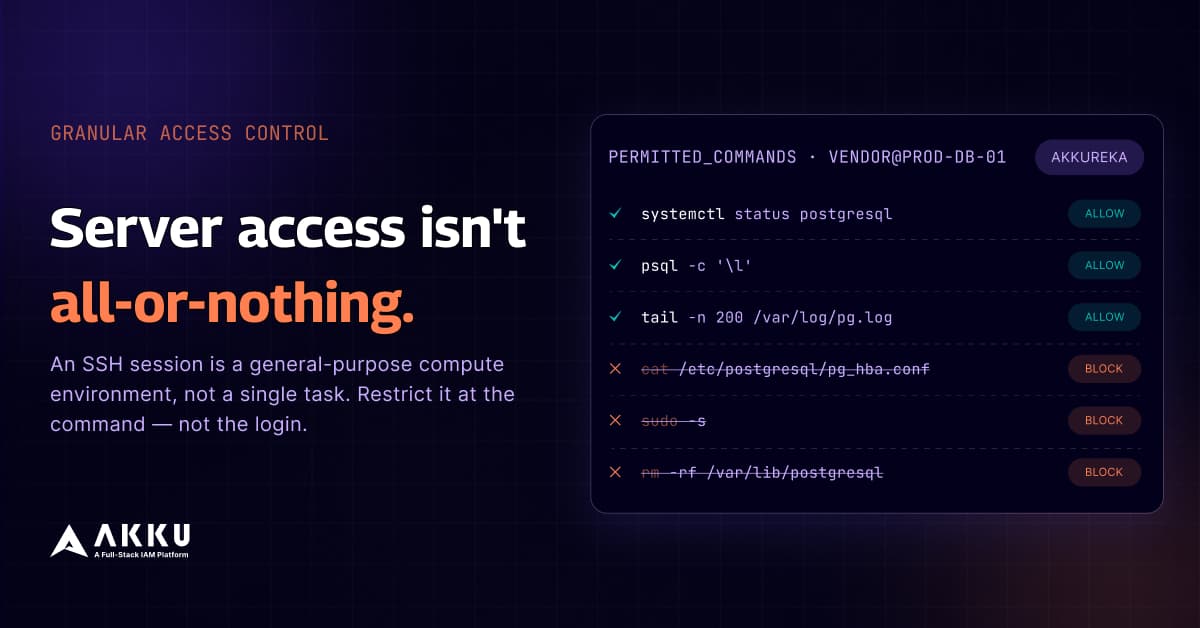
Server Access Isn’t All-or-Nothing. The Organisations Treating It That Way Have a Problem.
Yeswanth A

Server Access Isn’t All-or-Nothing. The Organisations Treating It That Way Have a Problem.

When you give someone SSH access to a Linux server, what exactly have you given them? Think about that carefully before answering. Because the instinct is to say “access to do the thing they were brought in to do.” But what the SSH session actually provides, absent any command-level restrictions, is an interactive shell with … Continue reading Server Access Isn’t All-or-Nothing. The Organisations Treating It That Way Have a Problem.

13 May 2026|11 min read
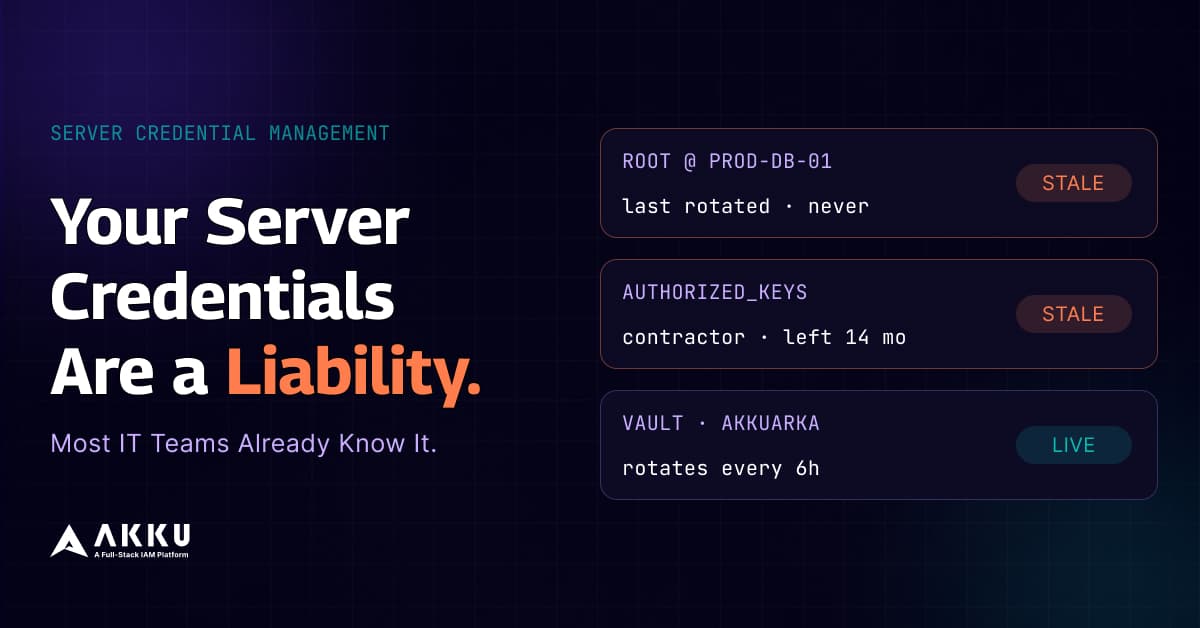
Your Server Credentials Are a Liability. Most IT Teams Already Know It.
Dinesh Harikrishnan

Your Server Credentials Are a Liability. Most IT Teams Already Know It.

When did you last rotate the root password on your most critical production server? Not when it was scheduled. Not when the policy says it should have been. When it actually happened, with a documented record, and with every system that depended on that credential updated at the same time. If that question made you … Continue reading Your Server Credentials Are a Liability. Most IT Teams Already Know It.

13 May 2026|11 min read

Keep in Touch

Sign up for our blogs