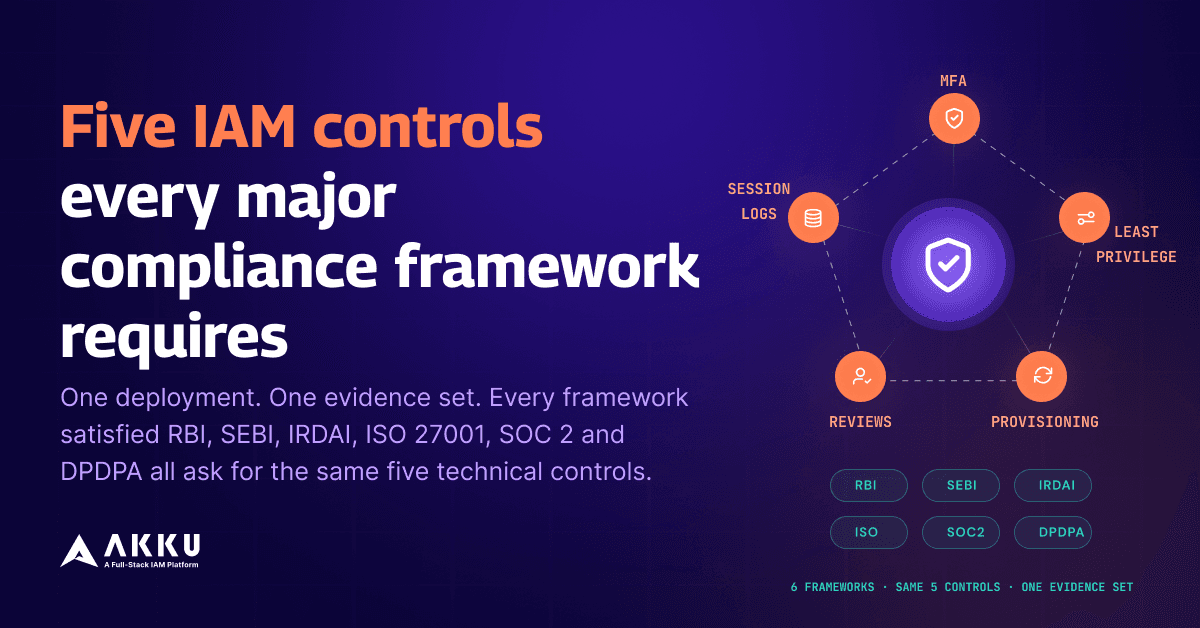
Five IAM Controls Every Major Compliance Framework Requires
Vinayak P

Five IAM Controls Every Major Compliance Framework Requires

Your organisation is likely operating under more than one compliance framework. RBI if you are a bank or NBFC. SEBI CSCRF if you are a capital markets entity. IRDAI ICS if you are an insurer. ISO 27001 if you are pursuing certification. SOC 2 if you serve enterprise clients. DPDPA if you process personal data … Continue reading Five IAM Controls Every Major Compliance Framework Requires
10 July 2026|13 min read
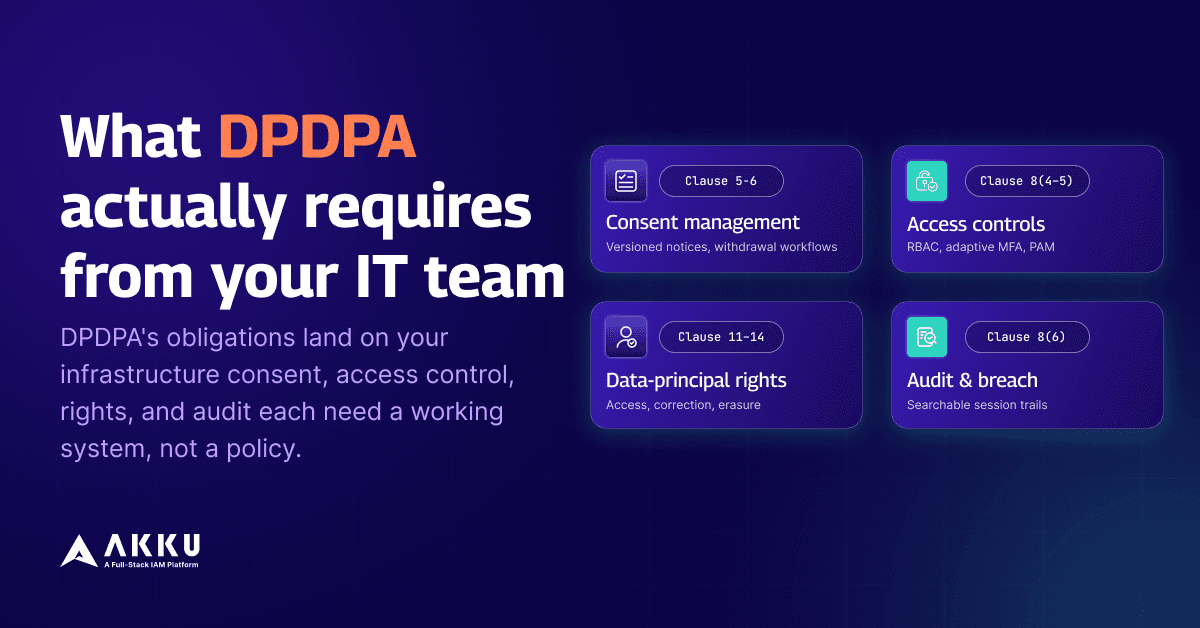
What DPDPA Actually Requires From Your IT Team
Vinayak P

What DPDPA Actually Requires From Your IT Team

The Digital Personal Data Protection Act, 2023 is not a policy compliance exercise. The obligations it creates land directly on your IT infrastructure. Consent must be captured, stored, and made withdrawable through a technical system. Access to personal data must be controlled and auditable. Data Principal rights including access, correction, and erasure require automated workflows … Continue reading What DPDPA Actually Requires From Your IT Team

06 July 2026|12 min read
Audit-Ready Organisations Don’t Prepare for Audits. They’re Already Ready.
Vinayak P

Audit-Ready Organisations Don’t Prepare for Audits. They’re Already Ready.

Here is a question worth asking your compliance team: how long would it take to produce the evidence package for your next ISO 27001 or SOC 2 audit if the auditor announced it today? If the answer is measured in weeks, your organisation is not compliant. It is compliant-looking, periodically, when someone assembles the evidence. … Continue reading Audit-Ready Organisations Don’t Prepare for Audits. They’re Already Ready.

15 June 2026|11 min read
Your Compliance Reports Are Only as Current as Your Last Manual Export
Vinayak P

Your Compliance Reports Are Only as Current as Your Last Manual Export

When did you last run a compliance evidence collection that did not surface something unexpected? Not a gap in your controls. Something more mundane than that. A SCIM connector that failed three weeks ago that nobody noticed because there was no monitoring on it. A provisioning record that shows an offboarded user as deprovisioned, but … Continue reading Your Compliance Reports Are Only as Current as Your Last Manual Export

22 May 2026|14 min read
How to Prepare for India’s New DPDP Rules and Safeguard Your Organization
SatyaDev Addeppally

How to Prepare for India’s New DPDP Rules and Safeguard Your Organization

The phased rollout of India’s Digital Personal Data Protection (DPDP) Rules officially began on November 14, 2025, marking the full operationalization of the DPDP Act, 2023. While organizations have an eighteen-month window for phased compliance, the complexity of managing digital identities means you must act now to avoid penalties that go as high as ₹250 … Continue reading How to Prepare for India’s New DPDP Rules and Safeguard Your Organization

10 February 2026|3 min read
ISO 27001 Implementation Guide 2025: How Akku Supports Your Compliance Journey
Vinayak P

ISO 27001 Implementation Guide 2025: How Akku Supports Your Compliance Journey

ISO 27001 certification is quickly becoming a baseline requirement for any organization that handles sensitive data. But implementing ISO 27001 and staying compliant is no small feat. With over 190 clauses and controls, most of which are technical and complex, the process can feel overwhelming. That’s where Akku comes in. Akku is a cybersecurity platform … Continue reading ISO 27001 Implementation Guide 2025: How Akku Supports Your Compliance Journey

01 August 2025|5 min read

Keep in Touch

Sign up for our blogs