Sales: +91 9600 70 3224
- Support


A cloud-native directory that can be your source of truth or defer to the one you already run.
Akku runs as your standalone primary directory, holding every workforce identity and attribute, or it sits alongside AD or LDAP and synchronises with whichever one you keep as the source of truth. Nothing about the rest of the platform changes either way. SSO, MFA, contextual conditions and monitoring work the same whether the identities live in Akku or in the directory you already have.
A unified cloud identity store centralises identity data in a cloud-native directory that provides a consistent, real-time source of truth for user profiles, group membership and application access across an organisation's IT landscape.
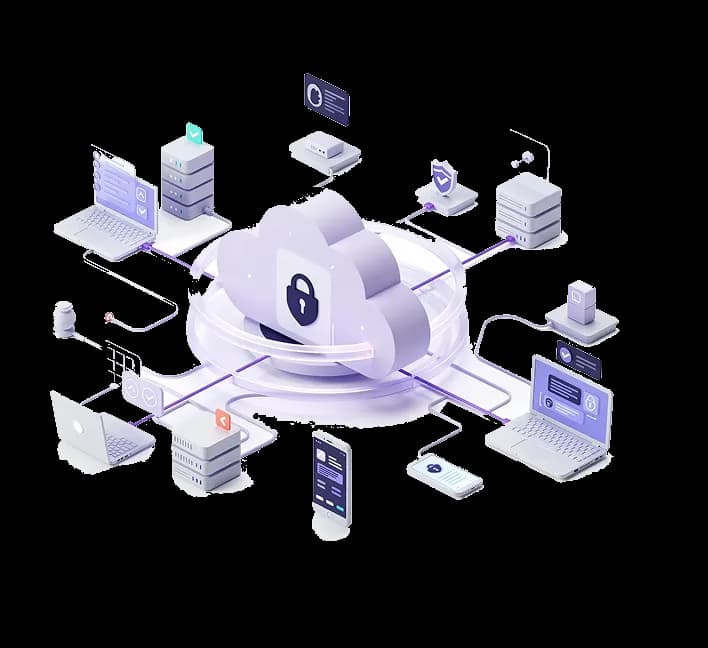
Directory synchronisation keeps every connected system, cloud, on-premises or hybrid, reflecting the latest user information and access rights. It brings multiple independent directories, identity providers and access systems into one manageable service that enforces uniform policy.
The directory holds every workforce identity with its attributes, and it is cloud-native rather than a cloud front end on something older. The schema extends with custom attributes for the things your business tracks that no standard schema anticipated: cost centre, shift pattern, licence number, whatever your access decisions actually turn on. Because those attributes live in the directory rather than in each application, they are available to contextual access conditions and to group membership without being re-entered anywhere. Applications draw identity from one place instead of each holding a partial copy that drifts.
A federation gateway extends identity across trusted domains and to external identity providers, which covers contractors on their own tenancy, an acquired business still running its own directory, and partners authenticating against something you do not control. The directory speaks the standard federation and authentication protocols, so a domain you trust does not have to be a domain you administer.
Synchronisation keeps identities consistent between Akku and the directory you have designated as the source of truth. Replication keeps the directory itself consistent across the systems reading from it. A change made once, a new starter, a role change, a leaver, reaches everything connected without being re-entered.